01
Isolated representative environment
Maps approved assets, identities, configurations, and dependencies into an isolated environment designed for validation and simulation.
Isolated mission-environment simulation for cyber resilience, exposure validation, dependency analysis, and mission hardening. Build and exercise a representative environment without requiring adversary testing inside production.
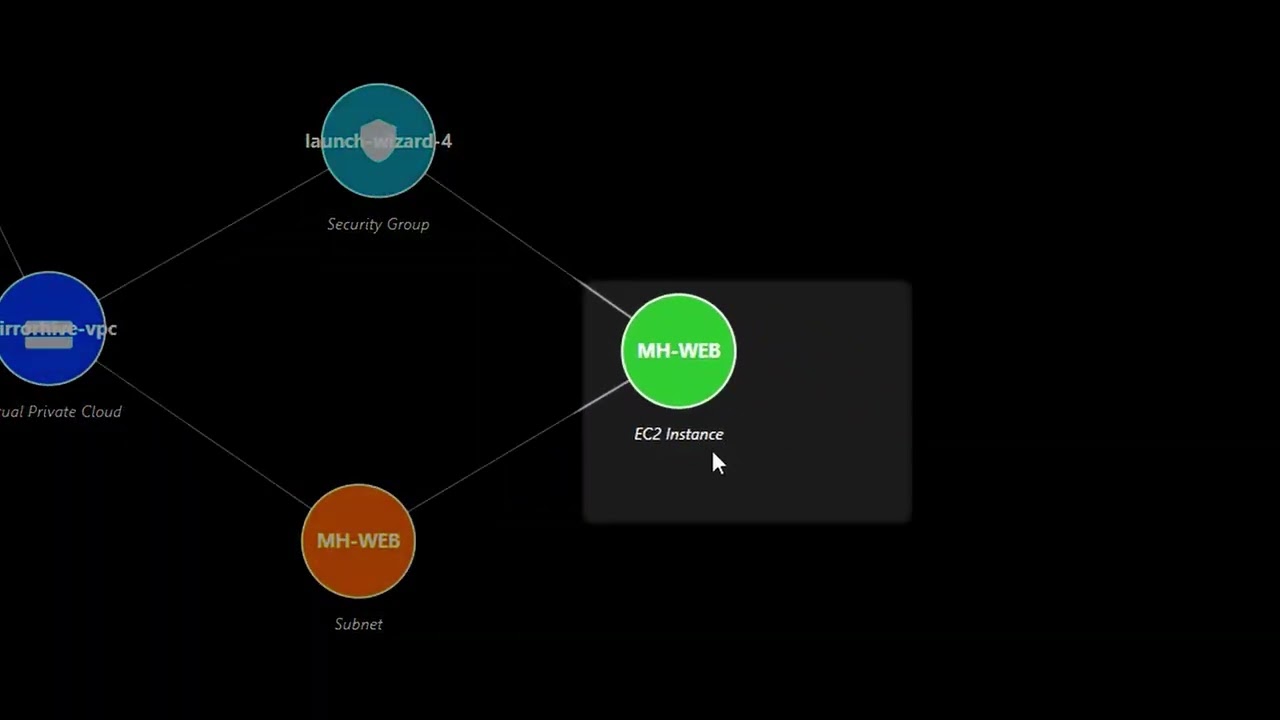
Live demonstration of what Mission Twin does in a federal cloud enclave. Production environment on the left remains untouched. An isolated mirror environment on the right runs AI-assisted attack simulations, surfacing kill chains, lateral movement, and compounding weaknesses in human-readable form.
Mission teams often cannot test cyber, data, and operational dependencies against adversary pressure without touching live systems or creating production risk. Penetration testing windows are short. Red-team scope is bounded. Dependency failures cannot be exercised in production. Adversaries do not face the same limits. The result is a tempo gap and a confidence gap at the same time.
Mission Twin creates an isolated representative environment using read-only discovery of approved source configurations and dependencies. Inside the isolated environment, teams can exercise adversary scenarios, dependency failures, attack paths, and hardening options without running those simulations against live production. This reduces the need to conduct high-impact testing in production.
Maps approved assets, identities, configurations, and dependencies into an isolated environment designed for validation and simulation.
AI-assisted simulation helps surface attack paths, lateral movement, dependency risk, and compounding weaknesses for engineer and operator review.
Outputs include exposure paths, dependency maps, validation findings, and mitigation options. Human operators and engineers remain responsible for decisions.
Human-readable mission risk, exposure paths, dependency maps, mitigation options, and readiness recommendations. Output is shaped for technical directors, mission cyber leads, and prime integrators to review, validate, and act on.
A visual preview of the Mission Twin environment for isolated mission simulation and exposure validation. An updated demonstration video will be published here.
Scout review, technical exchange, tabletop evaluation, representative-data validation, prototype-path planning, TSM, OTA, SBIR, AFWERX, or prime teaming. Pathway routing built in from day one.
Repeatable lab-validated behavior on isolated representative environments. Customer-operated, release-stage, and sustainment-ready claims used only where verified.
NSA / DIB Cyber. DoD Cyber. TSM. OTA. AFWERX. SOF Cyber. C5ISR. Prime cyber integration.
SDVOSB subsystem fit for prime cyber integrators with documented federal cyber-program work. Reduced capture burden for primes pursuing modernization contracts.
Mission Twin is presented as an unclassified, lab-stage capability. Claims about integration, certification, deployment, or operational performance require separate validation.
Federal cyber teams, NSA/DIB programs, SOF cyber, C5ISR, prime integrators: tell us the enclave and the operational lens. Axirix shapes the package to your evaluation criteria.